
Proof-of-Consent
A Privacy Proof-of-Consent documents that a visitor submitted a form (e.g., registration, contact, policy acknowledgment) that included your privacy consent text/checkboxes. When the configured form is submitted, the banner captures a snapshot of what was shown and sends a Privacy Consent entry to the application. The export includes:
- the property/app ID, internal user hash, session ID, and a unique consent_id,
- identifiers (IP address, and email/subject if collected), masked only where your anonymization settings apply (see below),
- the form_id that produced the entry,
- any checked_preferences (when your form defines multiple consent checkboxes), and
- a proof field containing the HTML snapshot of the rendered form content.
Why this matters: the proof gives you the exact text and structure presented at submission time, tied to stable IDs (consent_id , form_id , session_id ) so you can reference it in audits, DSR workflows, or vendor reviews. Check an export for identifiers before sharing it.
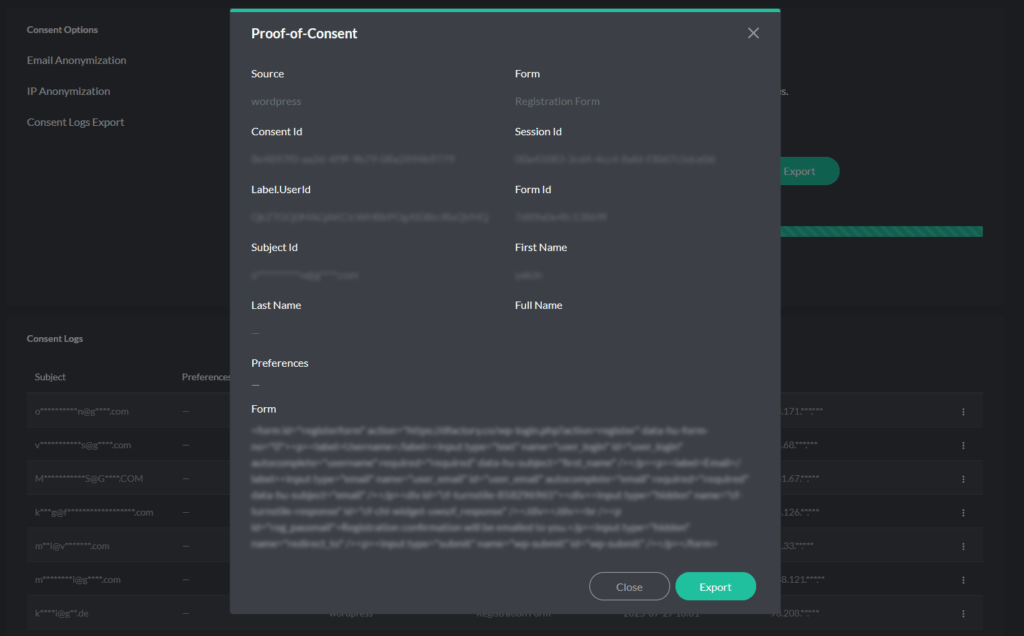
Generating a Proof-of-Consent
In the application, open Consent Logs and switch to Privacy Consent. Open the entry's 3-dot menu and choose Proof-of-Consent to view the record, or Export to download it (Export is not available on the Free plan). A single-entry export uses the row as shown in the logs view, so it follows your IP and email anonymization settings for the ip_address and subject_id columns only; the name, the proof markup and user_id are not masked. A date-range export from the Privacy Consent tab is not masked.
Proof-of-Consent export contents
A Privacy Proof-of-Consent export includes:
- app_id — property/app identifier.
- user_id — a pseudonymous identifier derived from the subject’s email; treat it as personal data.
- form_id — a fingerprint (hash) of the form’s HTML at submission time. The same form markup gives the same form_id; any change to the form’s HTML gives a new one.
- session_id — browser session identifier at submission time.
- consent_id — unique identifier for this consent record (primary key for correlation).
- ip_address — the full IP address is stored. With IP anonymization on, part of it is hidden in the logs view and in a single-entry export, but not in a date-range export.
- subject_id — the subject identifier if collected (e.g., email), stored in full. With email anonymization on, it is partly hidden in the logs view and in a single-entry export, but not in a date-range export.
- full_name — present only when the form collects it.
- checked_preferences — selections within the privacy form when multiple checkboxes exist.
- proof — HTML snapshot of the rendered form content at submission time.
What you use it for
- Audit evidence: show the exact notice text/form the visitor accepted, with timestamp and IDs.
- DSR/complaints: retrieve the precise record and the HTML proof for the individual in question.
- Vendor/legal reviews: share a CSV that includes the proof markup. Check an export for identifiers before sharing it; a date-range export is not masked.